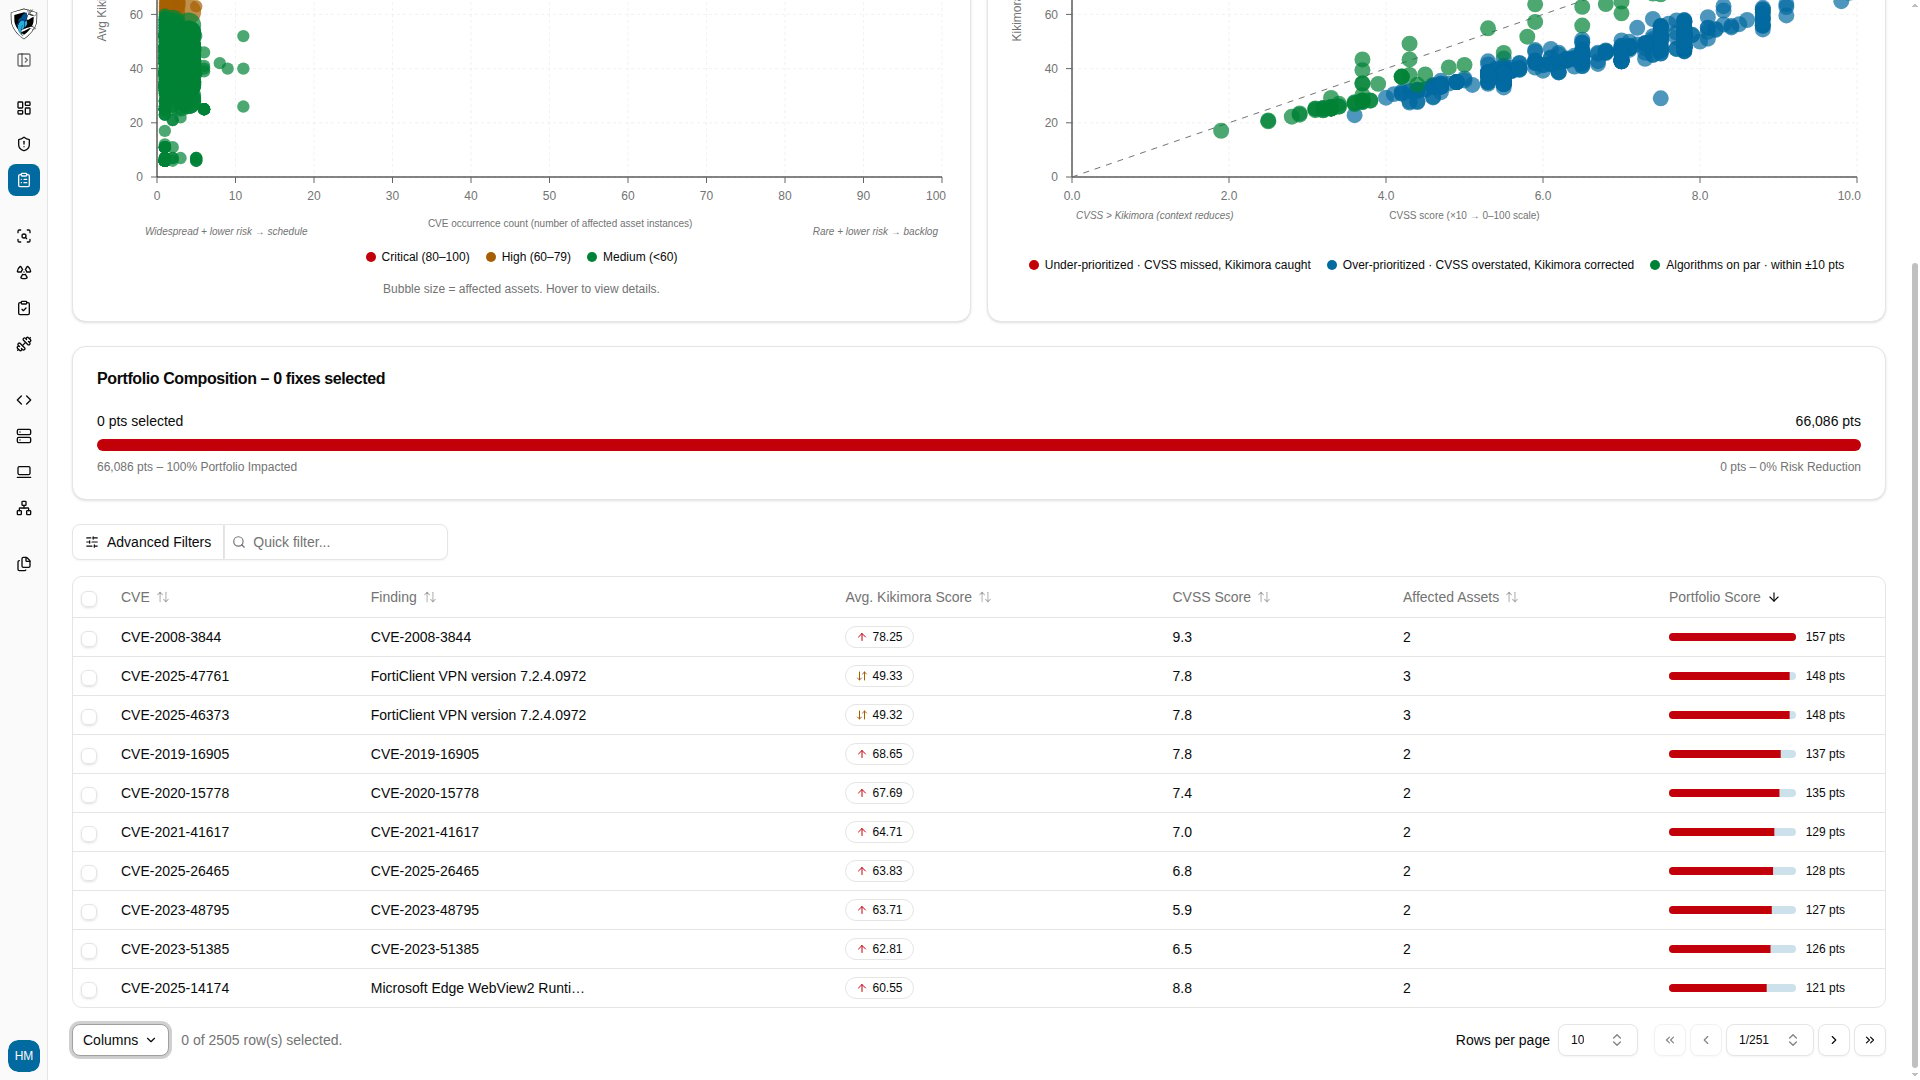
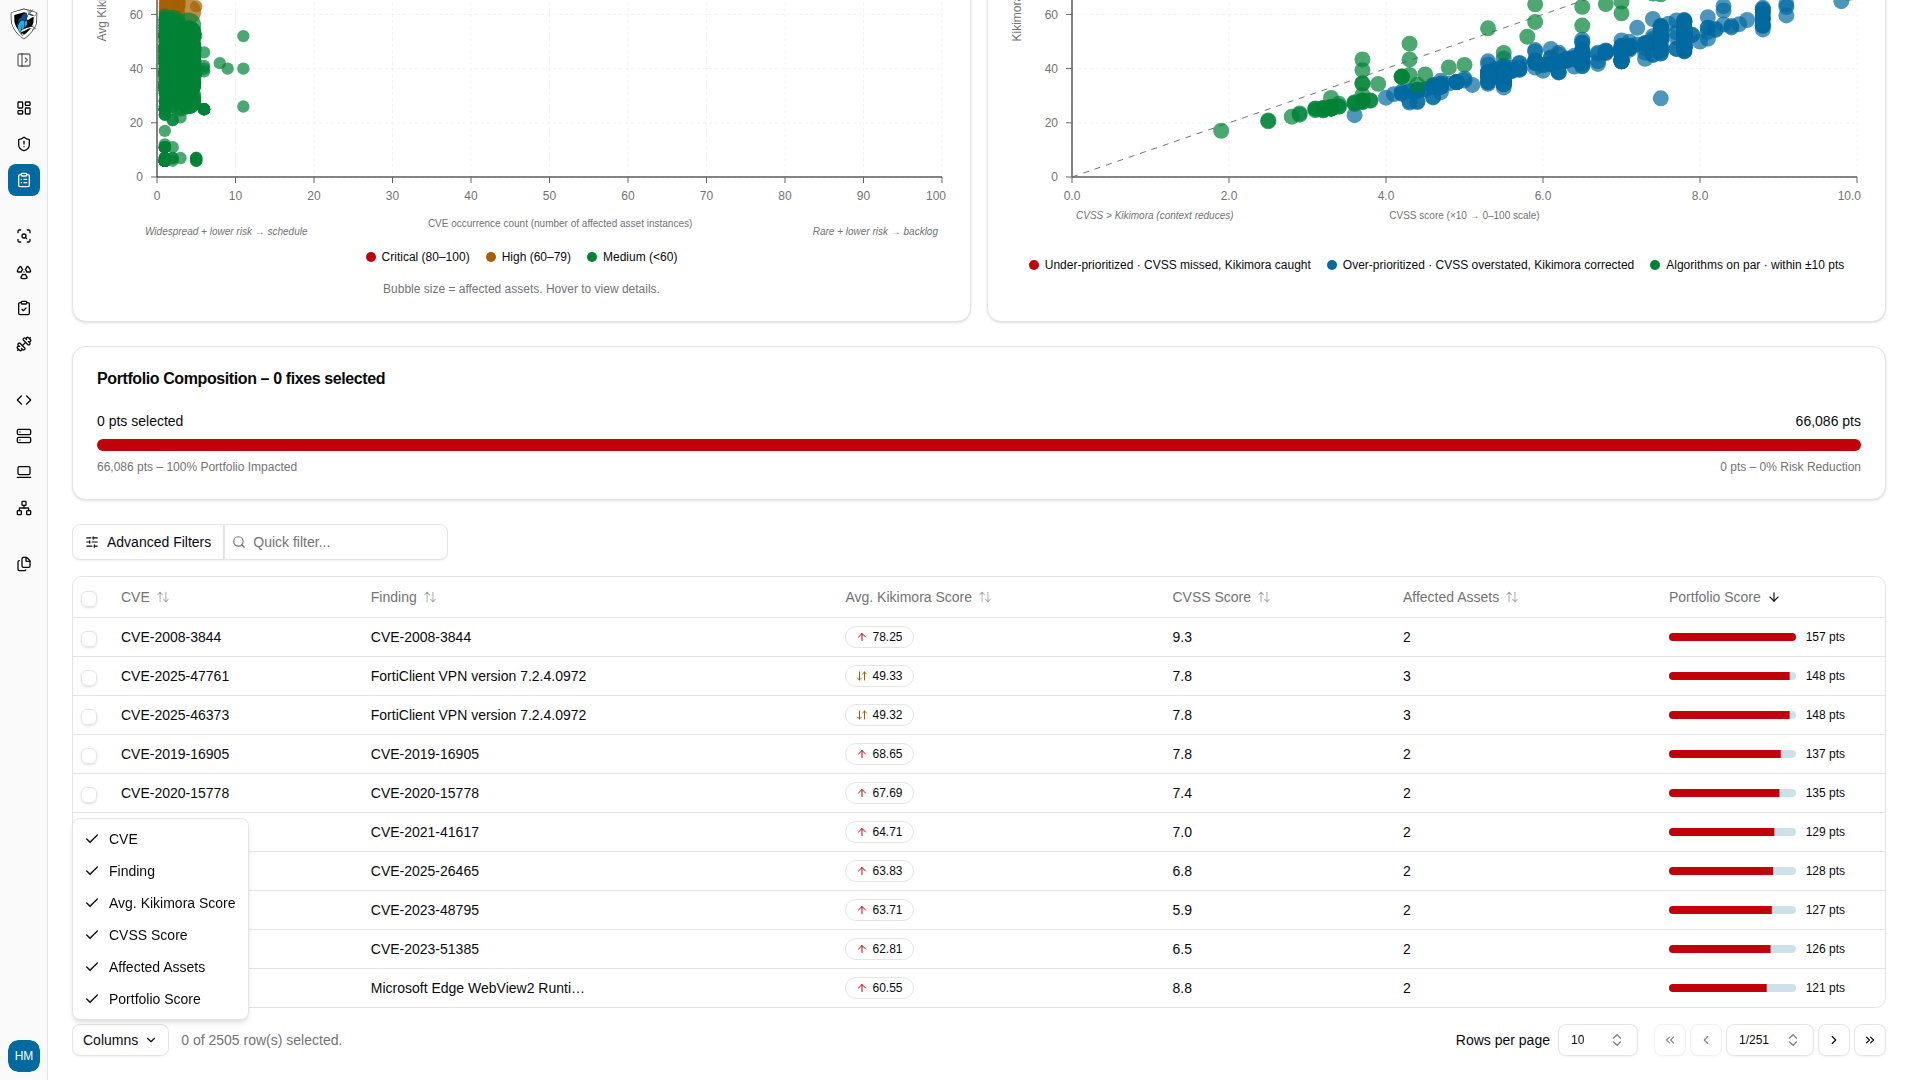
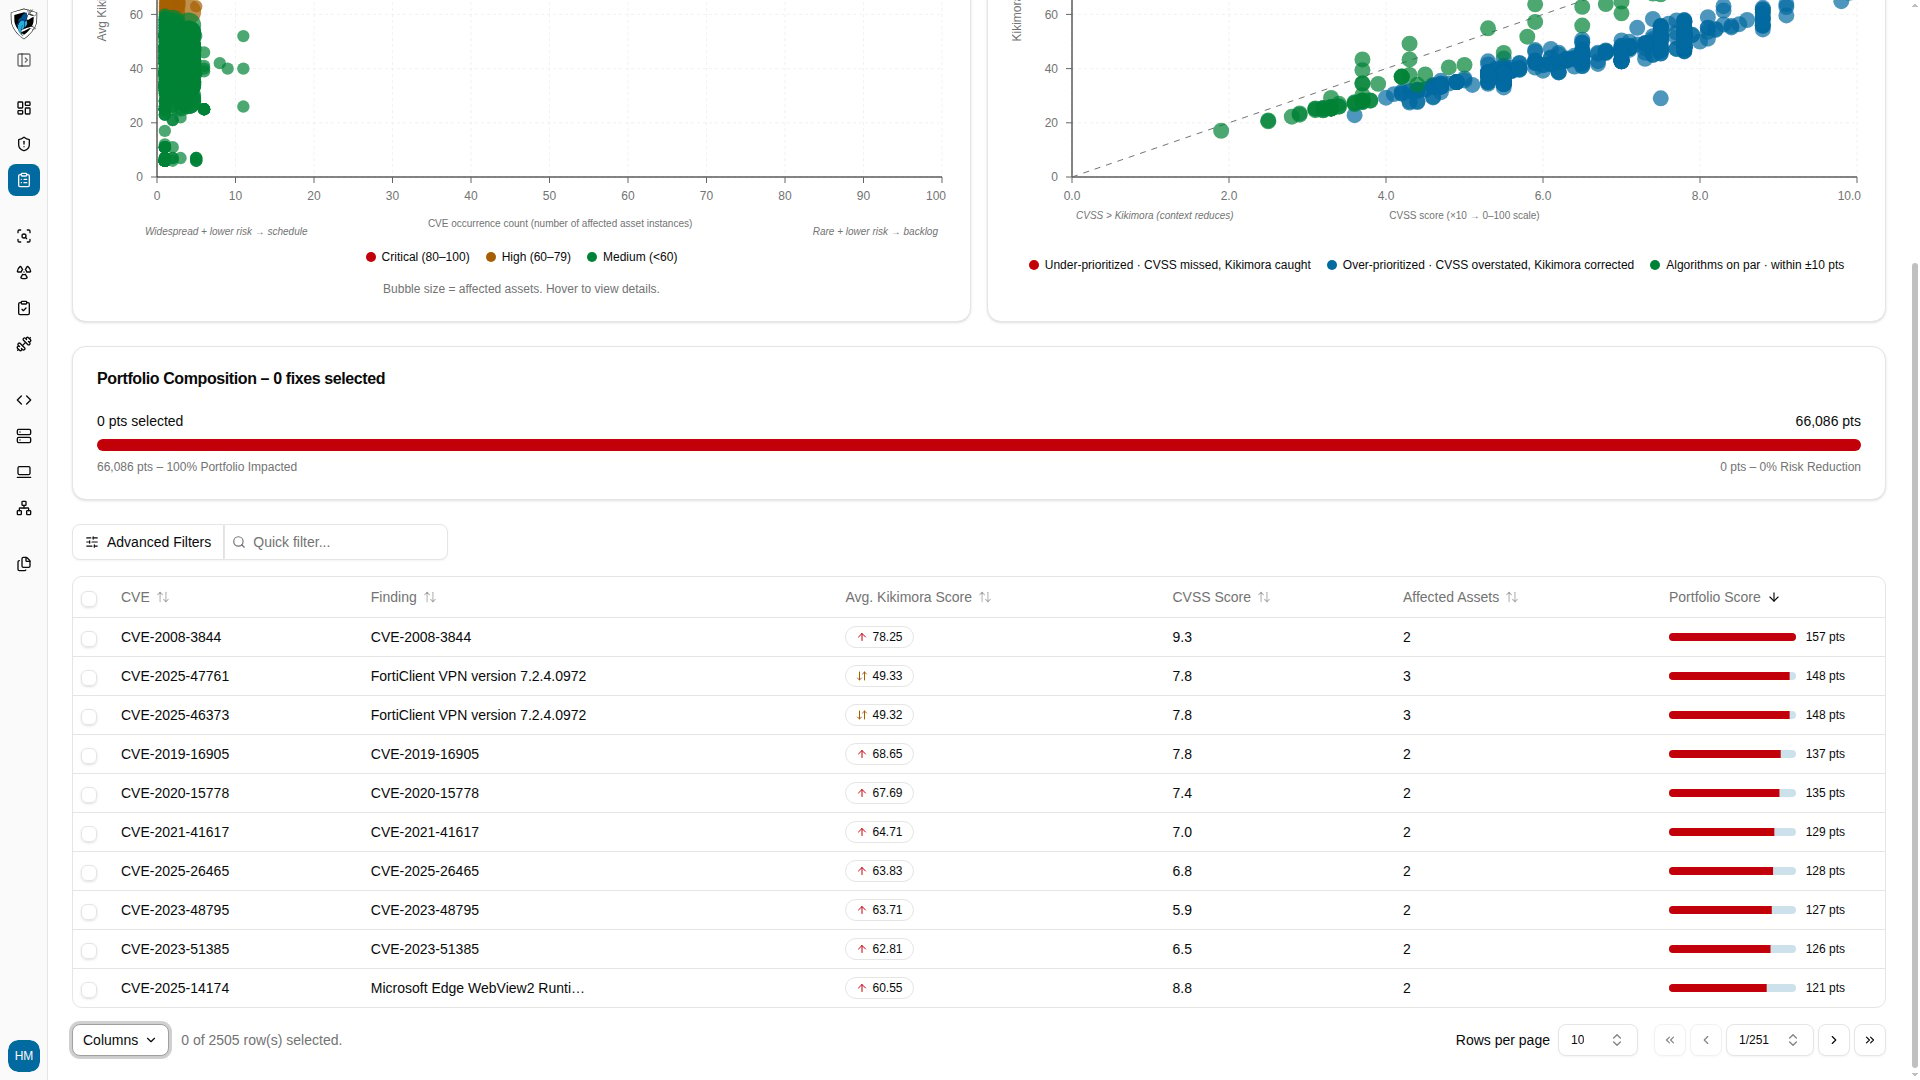
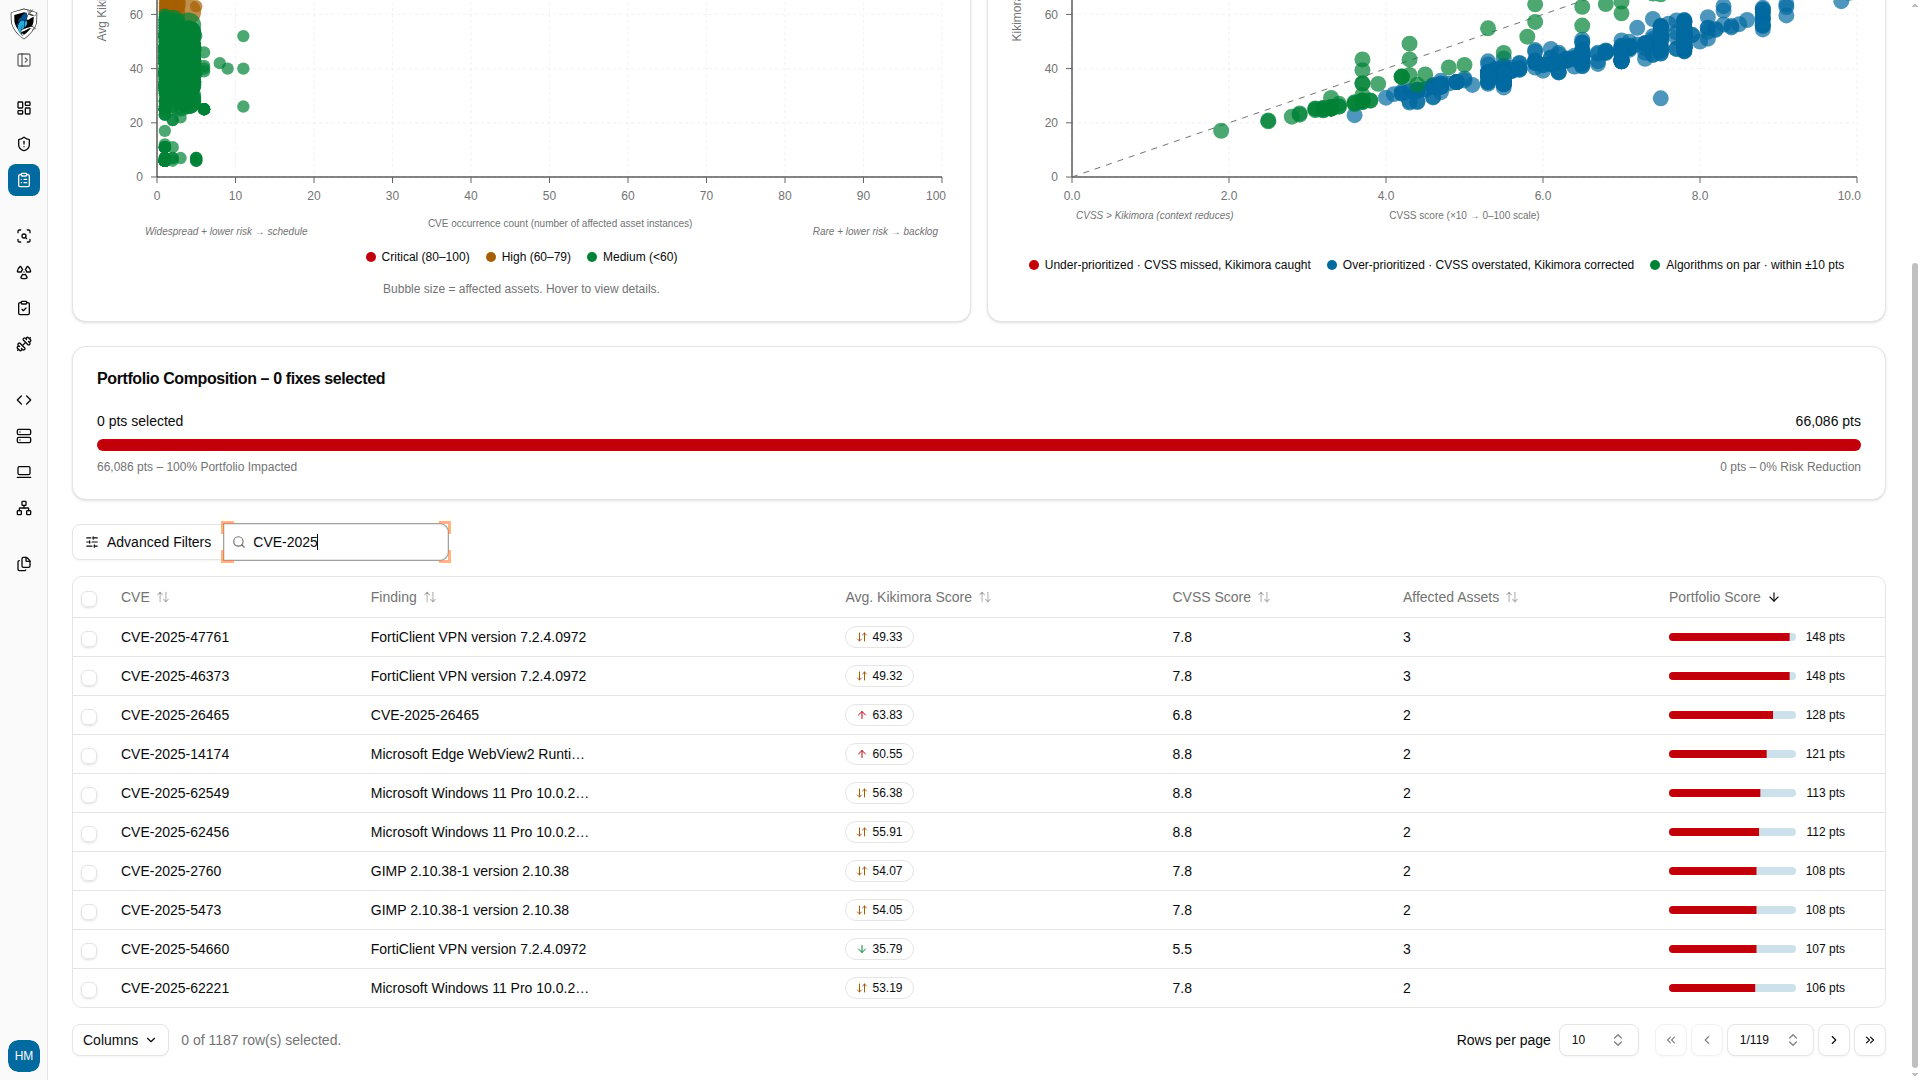
| CVE | Common Vulnerabilities and Exposures identifier, linking to the technical detail. |
| Finding | Name or summary of the affected component, package, or software version. |
| Avg. Kikimora Score | Context-aware risk rating (0–100) combining CVSS severity with asset exposure and policy compliance. |
| CVSS Score | Base CVSS severity score, on the 0.0–10.0 scale. |
| Affected Assets | Count of distinct connected endpoints affected by this finding. |
| Portfolio Score | Aggregated portfolio impact in points, reflecting total organizational risk. |